Organizations/Advisory & Compliance
Know where you stand. Know what comes next.
We help organizations understand cybersecurity risk, navigate compliance requirements and turn identified gaps into practical improvement plans.
Discuss Your Requirements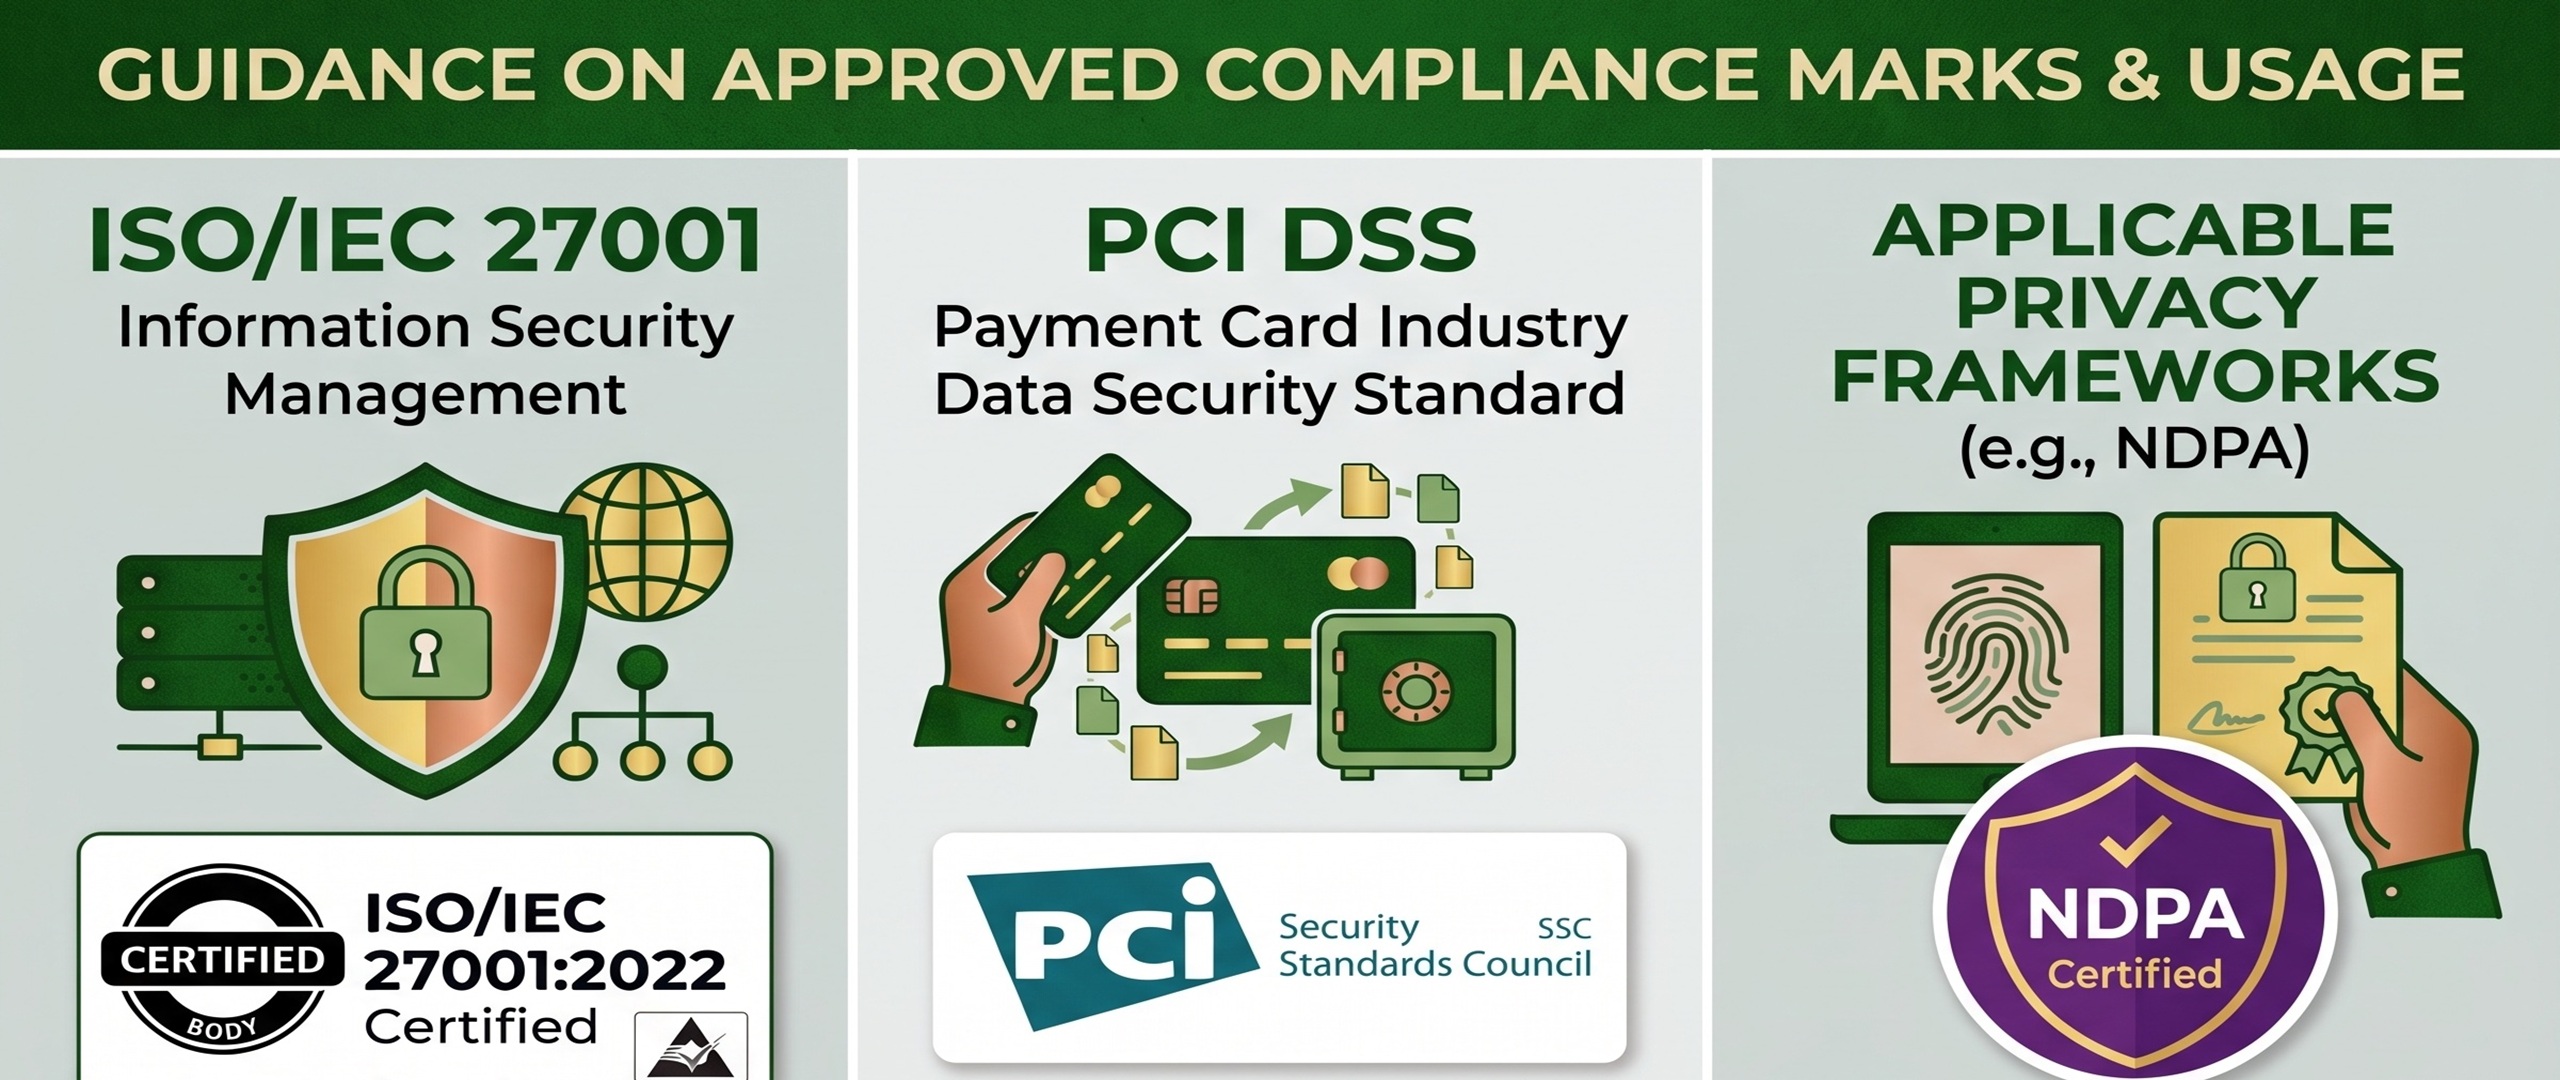
What we help with.
Cybersecurity Assessments
Understand the strengths, weaknesses and priority gaps across your security environment.
Risk Assessments
Identify, evaluate and prioritize security risks based on business impact.
ISO/IEC 27001
Scope, gap assessment, risk treatment, ISMS implementation, readiness and related advisory.
PCI DSS
Assess payment-security requirements, close control gaps and support compliance readiness.
Privacy & Data Protection
Help interpret requirements and strengthen data-handling practices and controls.
Governance & Policy
Build or improve security policies, standards, roles and governance structures.
Audit & Compliance Readiness
Prepare teams, evidence and controls for internal or external assessment.
Security Architecture Reviews
Evaluate whether current or planned security architecture adequately addresses business and technical risk.
How an engagement runs.
Understand business context, scope, regulatory requirements and existing controls.
Evaluate current state against relevant standards, risks and desired outcomes.
Separate urgent issues from long-term improvement work.
Support implementation or coordinate required corrective actions.
Review evidence and confirm readiness or improvement.
What you end up with.
Every engagement is written to leave your team able to carry the work forward without us.
- Clear understanding of current security posture.
- Prioritized roadmap rather than an undifferentiated list of findings.
- Stronger governance and documented controls.
- Better preparedness for audits and regulatory reviews.
- Practical recommendations that can be implemented.
Fix now Plan this quarter Improve over time
Findings arrive sorted into these three, because a flat list of issues is not a plan.
Frameworks we support.
List only frameworks Hacktales can genuinely support. Nothing aspirational ships here.


